A prototype can power up on the bench and still fail the moment it meets its real operating conditions, production process, or supply chain. That gap is where hardware design verification earns its place. It turns a promising circuit into an engineered product with evidence behind its performance, safety, manufacturability, and repeatability.
For product managers, founders, and R&D teams, verification is not a final checkpoint added before release. It is a structured process that informs engineering decisions early, when changes are faster and less expensive. For operations and procurement teams, it creates the technical certainty needed to plan components, production tests, quality controls, and product scaling.
What hardware design verification actually proves
Hardware design verification asks a direct question: does the product meet the requirements defined for it? Those requirements may cover electrical performance, power consumption, communications, environmental conditions, mechanical interfaces, safety functions, or production quality.
This is different from validation. Verification checks whether the design was built correctly against its specification. Validation checks whether the finished product solves the intended user need. A battery-powered sensor, for example, may verify against requirements for current consumption, radio range, and operating temperature. It is then validated by confirming that installers can deploy and use it reliably in the field.
The distinction matters because a product can pass one and fail the other. A technically compliant device might be difficult to install. Conversely, a useful prototype may lack the protection, tolerances, documentation, or test coverage required for series production.
Verification also cannot be reduced to a single laboratory test. It spans the circuit, PCB layout, firmware interactions, mechanical integration, assembly process, and test strategy. The extent of work depends on product risk. A simple controller board and a medical, industrial, or connected device will not require the same depth of analysis. The principle remains the same: decisions should be supported by measurable evidence rather than assumptions.
Start with requirements that can be tested
Verification becomes inefficient when requirements are vague. Statements such as “low power,” “fast communication,” or “works in harsh environments” provide direction, but they do not define a pass or fail condition.
A usable requirement is specific and measurable. Instead of “low power,” define maximum current in active, standby, and sleep modes at stated supply voltages and temperatures. Instead of “reliable communication,” state the protocol, expected range, data rate, interference conditions, and acceptable packet-loss rate. For an industrial input, define voltage range, surge exposure, isolation requirements, response time, and fault behaviour.
This discipline creates traceability. Each relevant requirement should connect to a verification method, a test result, the equipment used, and the responsible reviewer. A traceability matrix may feel formal during an early prototype phase, but it prevents a common late-stage problem: a team has many test reports yet cannot demonstrate whether every critical requirement has been addressed.
Requirements should also include production realities. Test-point access, programming time, marking, serialisation, acceptable component alternatives, and inspection criteria are not secondary details. They affect yield, serviceability, traceability, and cost from the first production batch onward.
Verify before the PCB exists
The best correction is the one made before a board is manufactured. Schematic review, calculation, and simulation reveal a large share of issues while engineering changes remain relatively simple.
At this stage, the focus is on architecture and component behaviour. Engineers review power sequencing, voltage margins, thermal dissipation, analogue signal ranges, protection circuits, clocking, interfaces, and failure modes. For power supplies, this may involve checking loop stability, load transients, inrush current, and derating. For high-speed or radio designs, signal integrity, impedance control, return paths, antenna placement, and electromagnetic compatibility need attention from the first layout decisions.
Component selection belongs in verification, not only purchasing. A part that works in a development build may introduce risk if it has a short lifecycle, limited availability, an unsuitable package, or a single-source dependency. Engineering and procurement should review alternatives early, particularly for products expected to remain in service for years.
The PCB layout then requires its own review. Correct schematics do not guarantee correct physical implementation. Creepage and clearance, copper widths, thermal paths, grounding, sensitive signal routing, panelisation constraints, fiducial placement, and assembly access all influence the final result. A layout that is electrically functional but difficult to assemble or inspect can create avoidable production losses.
Build verification around the real operating envelope
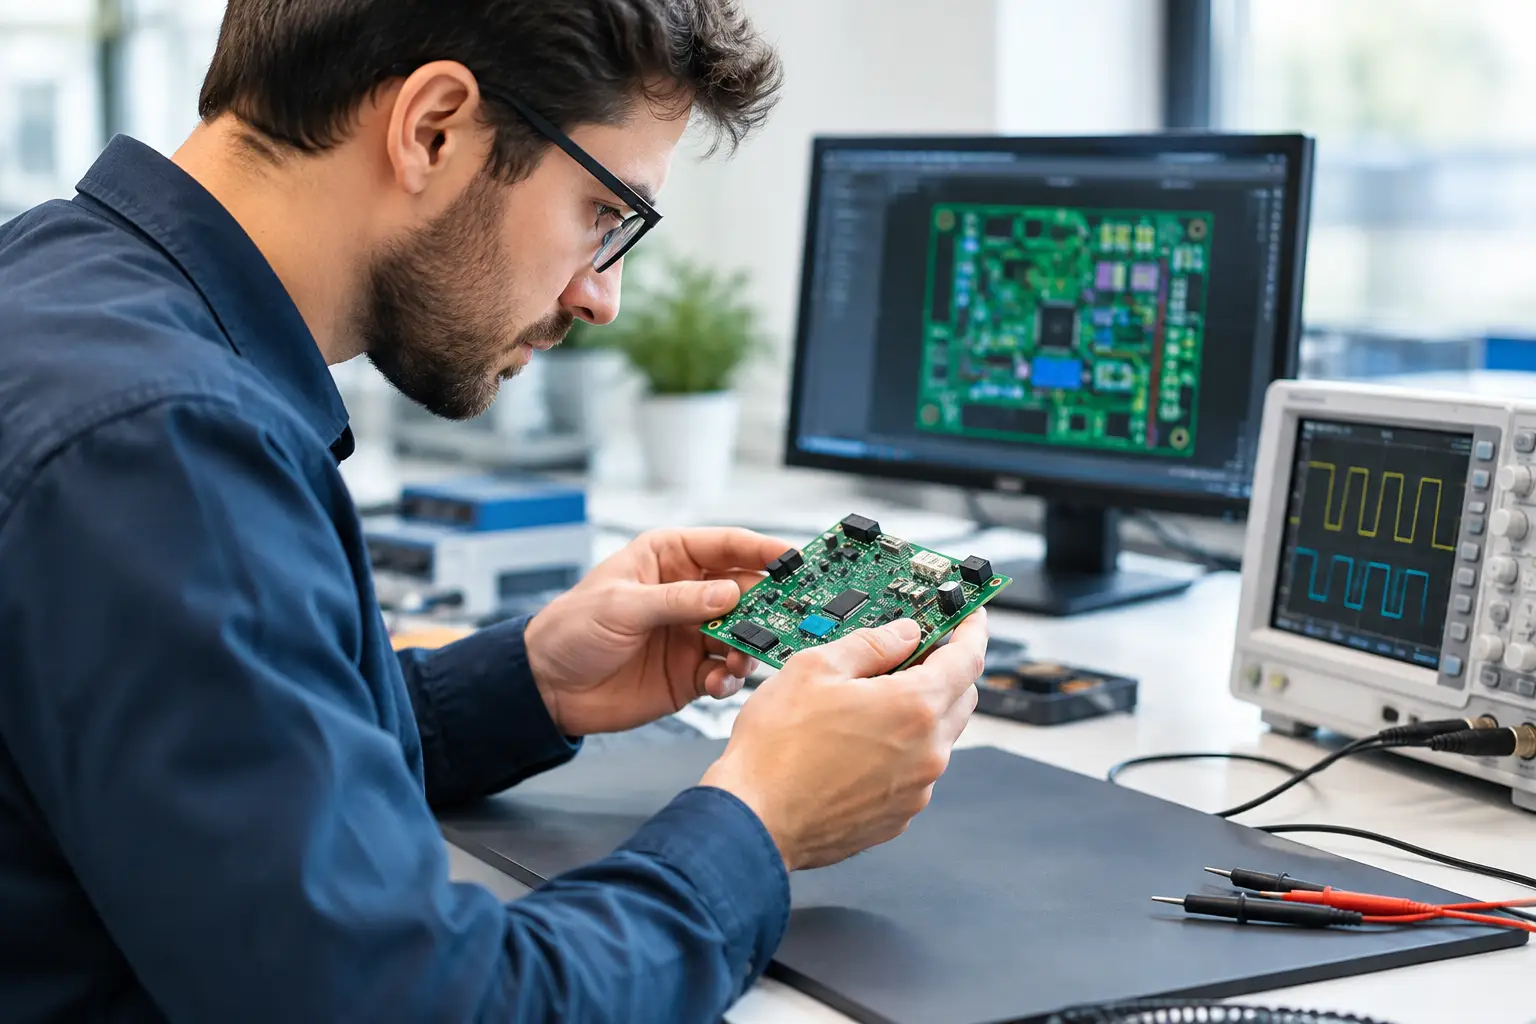
Bench testing should reflect how the product will actually be used. Testing only at nominal voltage, room temperature, and ideal loads creates false confidence. The important failures often appear at the edges: a depleted battery, a high ambient temperature, a noisy supply, a cold start, a connector partially inserted, or a network under load.
A practical verification plan normally covers functional operation, electrical margins, thermal behaviour, interfaces, fault handling, and environmental exposure relevant to the application. Where applicable, it should also include pre-compliance checks for EMC and radio performance. Discovering emissions or immunity problems after enclosure tooling, certification preparation, and production planning is costly because the solution may require changes across layout, grounding, shielding, cabling, firmware, or mechanics.
Firmware must be part of the picture. Hardware and embedded software influence each other through startup states, timing, configuration, watchdog behaviour, power modes, communication recovery, and factory programming. A design can pass a standalone circuit test but fail in operation because firmware activates peripherals in an unexpected sequence or does not manage a fault state safely.
Test methods should be repeatable. Record operating conditions, firmware version, board revision, instruments, fixtures, limits, and outcomes. This documentation supports engineering decisions, but it also prevents confusion when a product is revised or a field issue must be reproduced months later.
Design the production test while developing the product
A recurring mistake is to treat the production test as work for the end of the project. By then, missing test points, inaccessible connectors, slow programming procedures, and ambiguous pass criteria can force redesign or create an inefficient manual process.
Production testing should be defined alongside the hardware. The right approach depends on volume, product complexity, and risk. A low-volume industrial assembly may need a carefully documented functional test with calibrated instruments. Higher volumes may justify dedicated fixtures, automated programming, barcode-driven traceability, and data capture for each unit.
The aim is not to measure everything. Excessive test time increases cost and can introduce handling errors. The goal is to identify the failures that matter, distinguish assembly defects from design issues, and create confidence that every shipped unit performs as intended.
A useful test strategy considers four levels of control: incoming component checks where risk justifies them, optical and process inspection during assembly, electrical verification of the board, and final functional testing of the assembled device. Rework and repair processes should use the same traceability discipline. If a unit returns from the field, its revision history, test data, and component changes should be available to the team investigating it.
Treat prototype results as manufacturing input
Prototype builds are not merely demonstrations for customers or investors. They are opportunities to test the entire route from engineering data to assembled product. A small 0-series run can expose issues in bills of materials, supplier lead times, pick-and-place data, solderability, programming, enclosure fit, labelling, packaging, and functional test flow.
This is where close cooperation between engineering and manufacturing delivers a clear advantage. The people reviewing design choices should understand how boards will be assembled, inspected, tested, stored, and serviced. Manufacturing teams, in turn, need current design data and a defined process for handling deviations. Without this exchange, feedback arrives late and responsibility becomes fragmented across suppliers.
At Hemargroup, engineering, procurement, assembly, testing, and lifecycle services can be coordinated within one project flow. This helps teams move from prototype to industrialisation without losing the decisions, test knowledge, and traceability built during development.
When verification needs to go further
Not every device requires the same test depth. A non-critical internal accessory may need focused functional and manufacturing checks, while a product used in industrial control, healthcare, transport, security, or demanding outdoor environments requires more extensive evidence.
The appropriate level depends on intended use, applicable standards, expected lifetime, safety consequences, annual volume, and service model. A product with low annual volume but a costly field intervention may justify significant verification investment. Equally, a high-volume consumer device may need automated test coverage because even a small defect rate becomes expensive at scale.
The key is to make the risk decision explicit. If a test is excluded, the reason should be documented. If a requirement cannot be verified fully before release, define the residual risk, the mitigation, and the follow-up action rather than allowing an assumption to become an undiscovered product weakness.
The most useful outcome of hardware design verification is not a folder of passed test reports. It is a product team that knows what has been proven, what has changed, and what to watch as production grows. That knowledge gives the next prototype, the first series build, and every later revision a far stronger starting point.